


Smarter SIEM with AI, CMDB Insights, and Risk-based Precision
SecureVisio SIEM delivers full triage capabilities, including data collection, normalization, and enrichment. Our proprietary correlation engine correlates asset information from the CMDB and risk scores with SIEM alerts, providing context and high-impact threat prioritization tailored to your environment —all with AI guidance at every step.
Request a demo
A New Class of SIEM
AI-Assisted Detection and Triage
SecureVisio AI helps with alert triage by helping in assessing false positives and delivering detailed insights at machine speed. Our AI solution supports search, data onboarding, summarization, and action recommendations.
Dynamic attack path generation
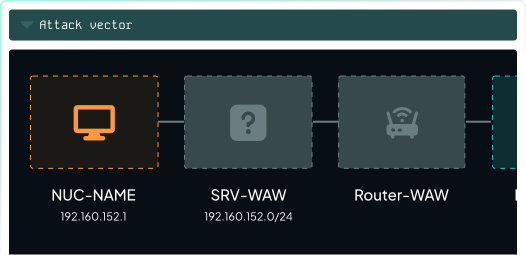
Thanks to integration with our internal CMDB, each SIEM alert includes a generated attack path that shows security teams how attackers could exploit your infrastructure—from the initial entry vector to the compromise of critical assets.
Know your crown jewels
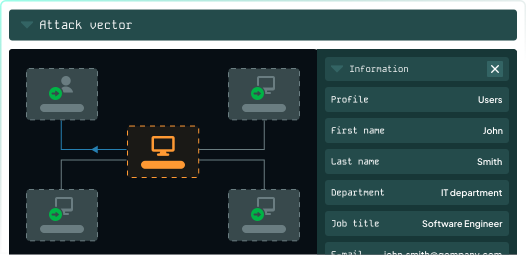
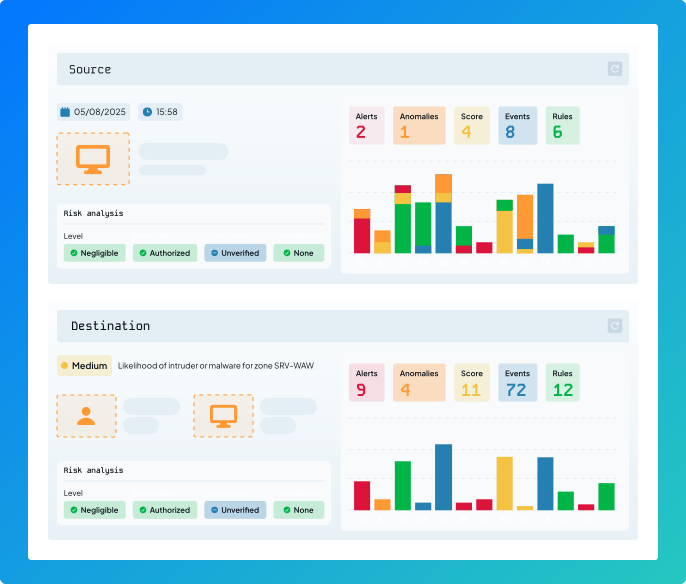
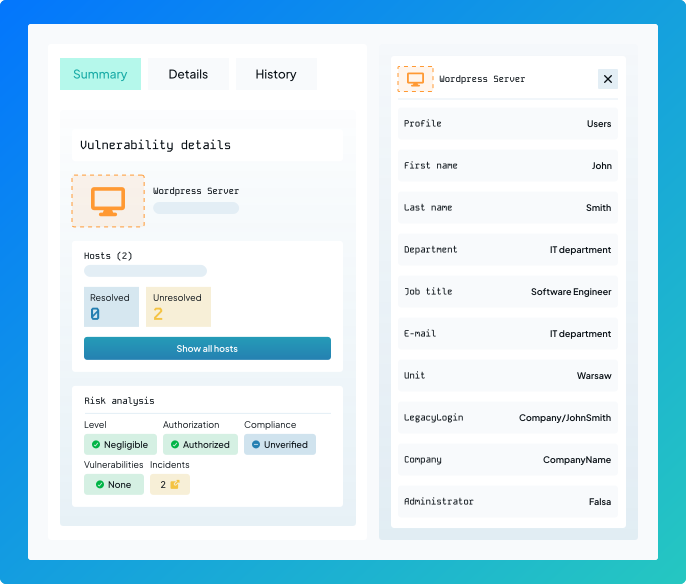
Through integration with the CMDB, BIA, and risk management modules, SecureVisio enriches each alert with data such as asset criticality, system ownership, network location, and related business processes.
See the full picture with backtracking
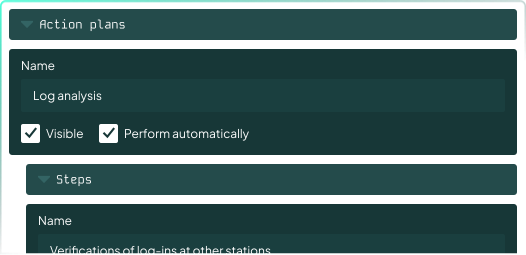
SecureVisio’s backtracking performs a broad assessment of affected assets for suspicious host or user activity, then checks source logs for security violation indicators, and finally correlates all related events to reveal threats, anomalies, and security gaps.
Powerful correlation engine and detection capabilities
Our SIEM integrates and correlates external and internal data sources, including the CMDB, risk scores, IoCs, BIA, and third-party cybersecurity tools. Data can be ingested via syslog, APIs, built-in XDR agents, and preconfigured connectors. Users can leverage over 500 out-of-the-box detection rules, deep MITRE ATT&CK mapping, and extensive user and entity profiling capabilities.
Unified Schema for Smarter Threat Detection and Easy Data Onboarding
With AI-assisted parsing and rule-writing, SecureVisio transforms raw logs into actionable intelligence, accelerating threat detection and response. Its SQL-like schema is intuitive and flexible, offering a wide range of predefined fields and options—such as CMDB assets and other contextual data—for easier, more powerful correlation and analysis.
Search, Correlate and Defend.
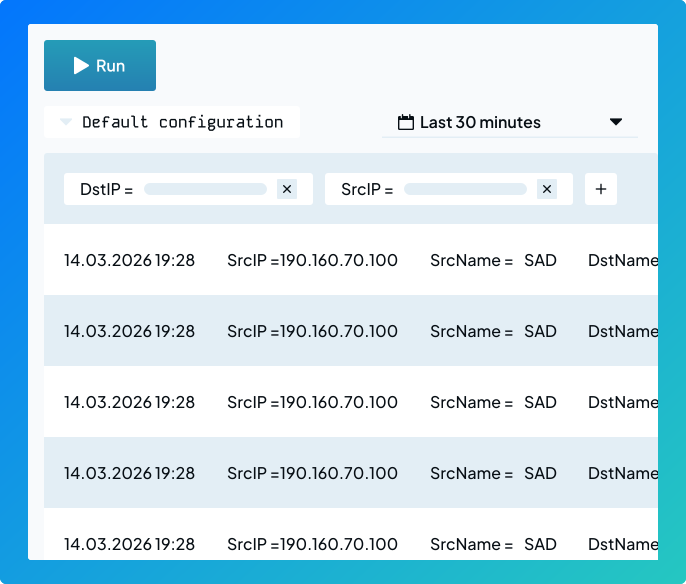
SecureVisio enables powerful search queries and active threat hunting through an intuitive, customizable log and event browser. Analysts can easily filter, correlate, and explore data across multiple views—table, text, or raw frame—using dynamic, SQL-like queries that simplify investigations and accelerate the detection of security incidents.
We are different class of
SIEM solutions

Available in both cloud and
on-premise

AI assistance streamlines workflows and accelerates the learning curve

Great base for cybersecurity programmes like CTEM

Incident, risk and vulnerability management inside one platform lowers TCO


