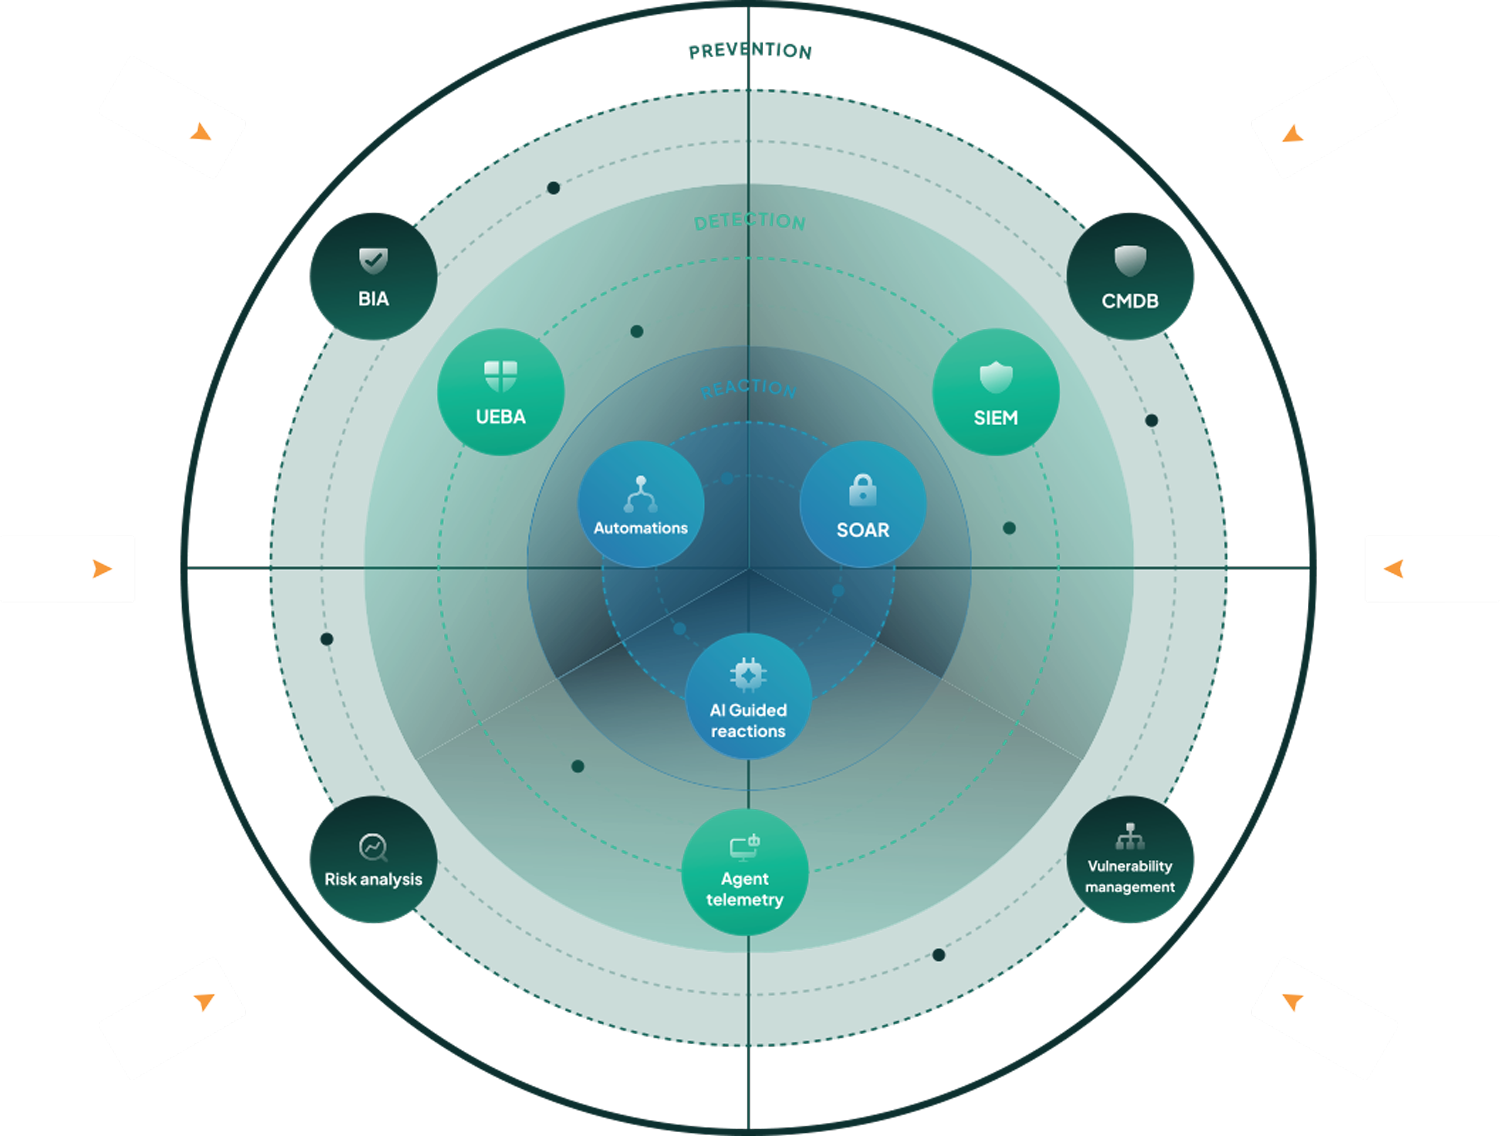
Traditional SIEMs are not architected for today's challenges
We believe that a fundamental change is needed in the world of SIEMs. Your security team needs to be equipped with context, risk-based prioritization, and AI to be effective in threat handling.
Request a demoFind out more
It’s time to finally transform incident and vulnerability
handling – with context, risk-based prioritization, and AI.
66%
of SOC teams can’t keep pace with alerts (SANS)
84%
of security professionals report feeling burned out (SANS)
Manage incidents better with context and AI-guidance
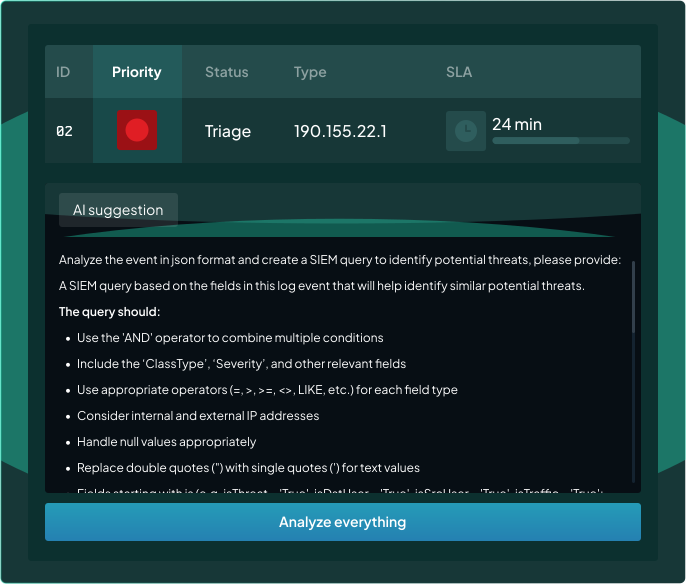
On top of the traditional SIEM detection and analysis capabilities, SecureVisio empowers security teams with contextual insights and risk information. The AI guides analysts by i.a. suggesting optimal parsing approaches, proposing threat-hunting queries, and producing concise summaries and recommendations.
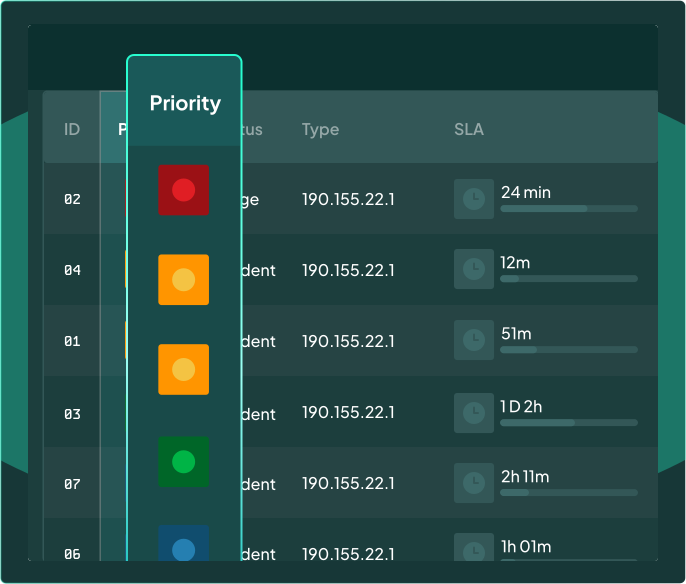
Prioritise threats by risks – no more guesswork
SecureVisio enhances vulnerability prioritisation by combining scanner-reported severity with organisation-specific risk weighting. The priority returned by vulnerability scan reports is multiplied by SecureVisio’s internal priority and further adjusted using built-in vulnerability prioritisation rules. This results in a risk indicator that reflects the actual relevance of a vulnerability to a given organisation.
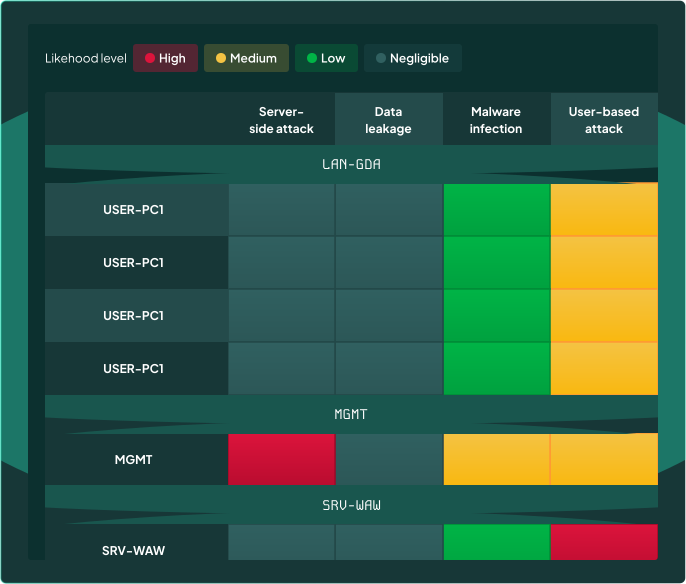
Perform risk analysis and gain visibility into BIA and cyber assets within one SIEM platform
SecureVisio is not just a SIEM-class tool—it’s a unified platform built from scratch with integrated risk analysis and a CMDB. The risk analysis module evaluates specific assets, identifies the likelihood of particular attacks, recommends safeguards, and assesses the consequences of breaches. The CMDB enables visualization of the entire logical infrastructure in an interactive and transparent way.
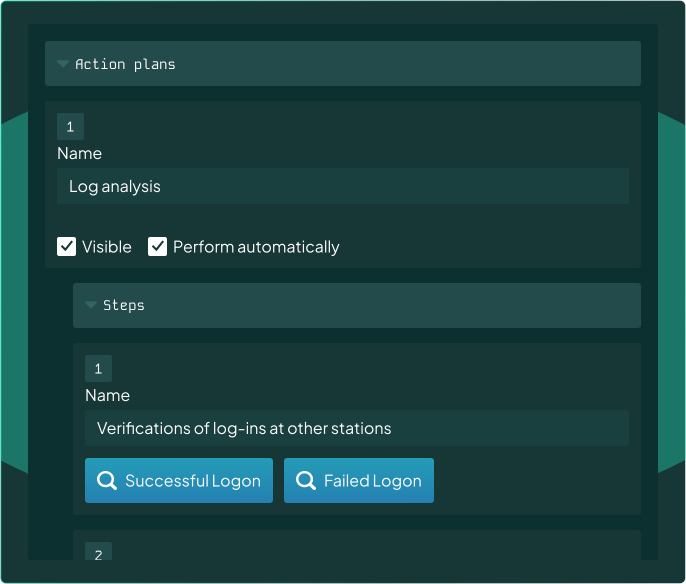
Real automations
Instead of dozens of manual steps and endless console hopping, the analyst simply reviews an enriched incident card. SecureVisio doesn’t just alert—it acts. The platform can perform parallel actions, from querying Active Directory and checking IoCs to correlating system and network logs to analyze sequential attacks.