


Integrated CMDB & BIA for Complete Cyber-Asset Visibility
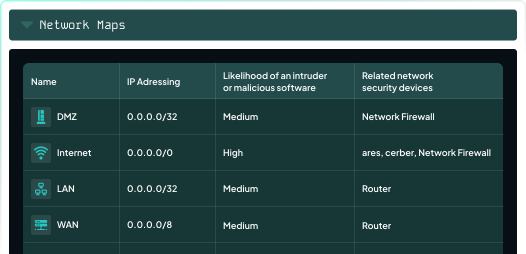
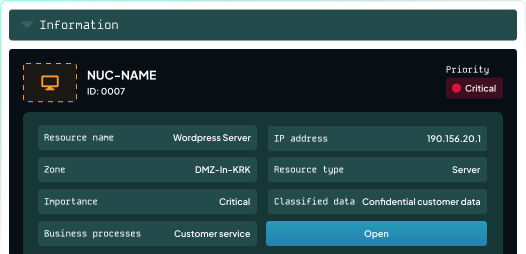
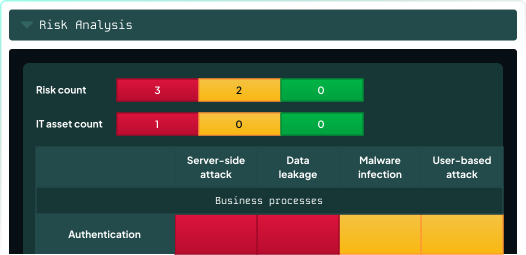
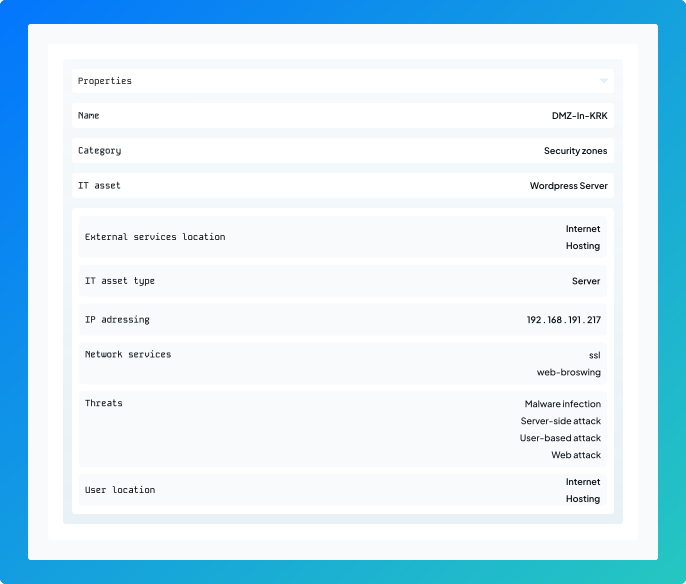
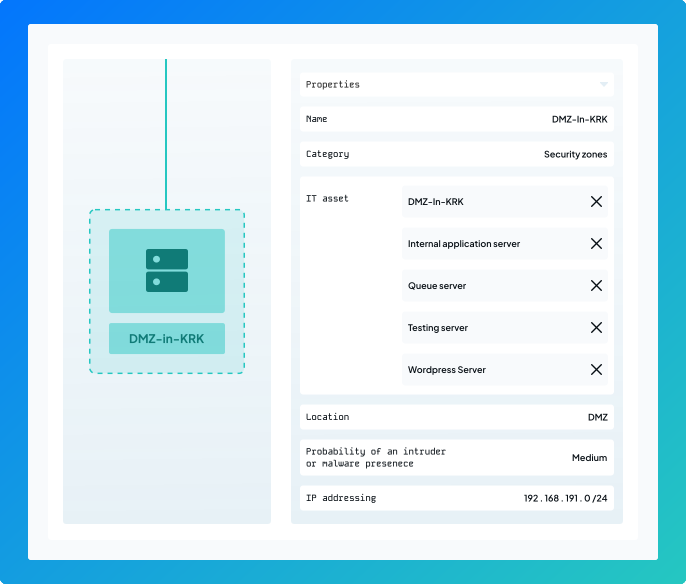
SecureVisio unifies asset inventory and business impact analysis in one single platform providing complete visibility across all cyber assets and the processes they support. The system allows to enrich each asset with threat categories, network details, software versions, data types, dependencies, and process participation—eliminating shadow IT.
Request a demo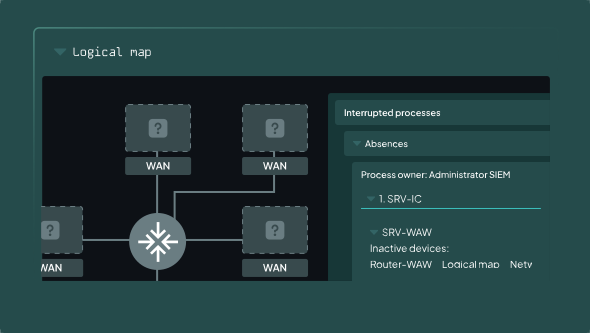
Behavioral Insights That
Accelerate Detection
Unified monitoring of host and user behavior
UEBA provides integrated visibility into both infrastructure/service resources (hosts) and users. Correlation rules for hosts and users are presented within a unified interface, enabling quick comparison of events, behavioral profiles, and security context.
Context-rich correlation rule insights
Each rule displays detailed information: the number of events detected, the hosts or users involved, their associated profiles, and a graphical timeline of activity. The system also indicates whether a rule can trigger an incident — and in which context (source, target, or user).
Interactive exploration and investigation
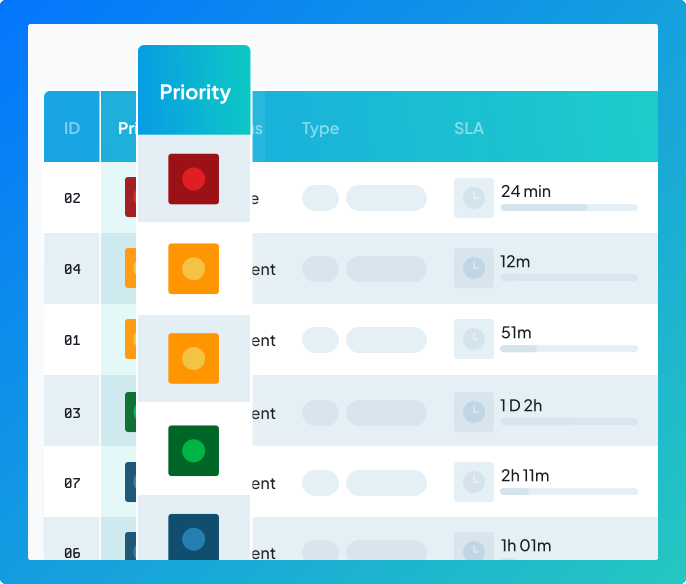
Analysts can interactively browse hosts or users associated with a selected rule. Inline filters, sorting, and context menus enable fast transitions to log viewers, event explorers, attack vectors, or management actions such as excluding a host/user or lowering event priority.
Rule editing with built-in classification
Rules can be edited directly from the interface using an integrated editor. UEBA supports classification views based on the internal SecureVisio categorization or the MITRE ATT&CK framework, helping analysts understand the tactics and techniques linked to detected activity.
Flexible time-range and data-scope controls
Operators can adjust the analysis window (today, yesterday, specific date, hourly range), switch between multiple LogCollectors, and choose the number of displayed entries. Data can be reloaded instantly whenever parameters change.
Seamless transition to deep investigation
Analysts can build filters based on detected anomalies and navigate directly from a user to relevant logs, EBA/UBA views, or detailed host/user lists. Each object can be investigated individually, with quick access to all related events, incidents, or behavioral profiles, and threat-hunting actions can be executed directly from the filtered view for faster, targeted investigation.
Graphical insight into behavioral patterns
UEBA provides visual timelines showing event distribution within the selected range or from archived periods. This supports rapid identification of anomalies, unusual activity patterns, and trend comparison across different days, weeks, or months.
Explore and Investigate
Behavioral Anomalies

Deep visibility into both infrastructure/service resources and users

Seamless transitions from UEBA to threat hunting

Simple rule editing with interactive host and user browsing

Context-rich correlation rules


