


Automate Cyber Risk Management
SecureVisio offers a comprehensive risk matrix for all cyber assets, delivering critical insights to evaluate risks, including likelihood, risk profiles, dependencies, consequence analysis, and recommended safeguards.
Request a demo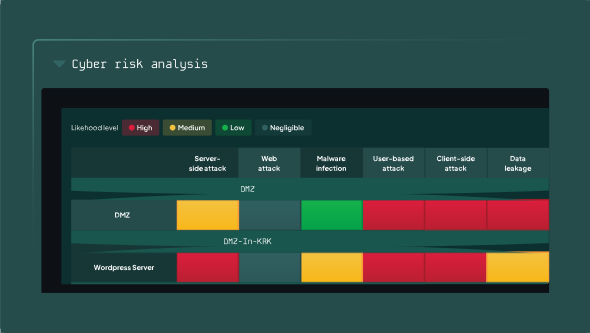
Know and Act
on Your Risks
Comprehensive cyber-risk visibility
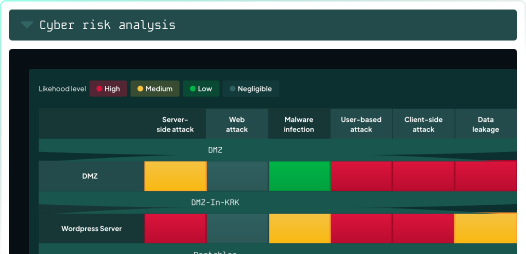
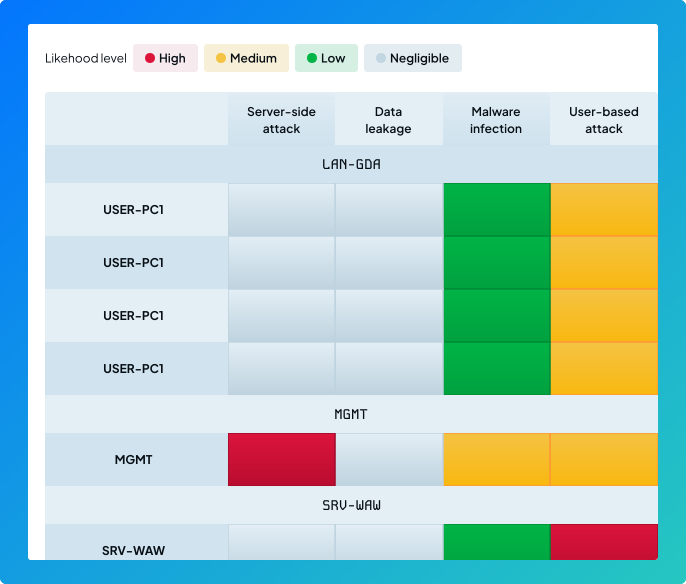
SecureVisio computes cyber-risk independently for every IT system, using logical maps as the foundation. It visualizes threats, affected assets, and business processes in intuitive risk matrices that highlight the most critical exposure points.
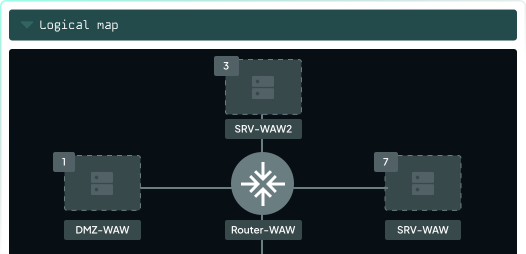
Deep, context-rich analysis of assets and processes.
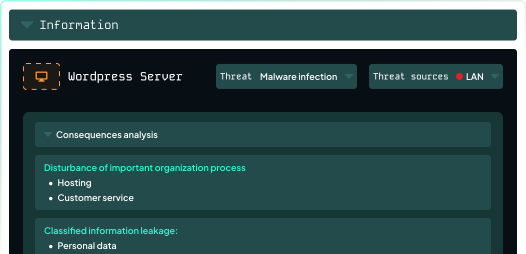
Each risk entry can be drilled into, revealing asset details from CMDB, processed data types, applied and missing safeguards, business process dependencies, and even attack vectors across security zones. Analysts immediately see why risk is elevated and what drives it.
Integrated view of consequences and safeguards
SecureVisio brings together all elements influencing risk — potential consequences, suggested and applied safeguards, data sensitivity, and business impact — in a single analysis window. This unified perspective helps analysts quickly understand why a threat matters and how well the asset is currently protected.
Actionable guidance for risk reduction
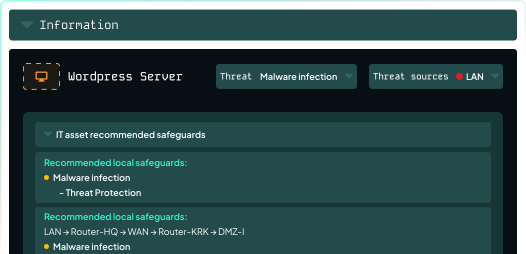
SecureVisio not only identifies high-risk areas but also proposes concrete local and network safeguards that reduce likelihood, or highlights where business processes should be redesigned to lower impact. This transforms risk analysis into a practical roadmap for security improvement.
Single source of truth for all cyber assets
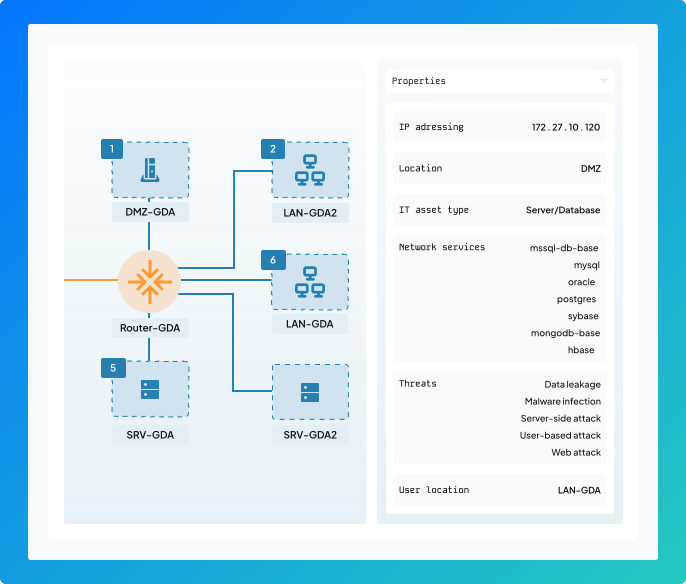
SecureVisio maintains a unified inventory of every information ensuring that risk analysis is always rooted in complete and reliable data. By automatically and manually assigning threat categories, IP addressing, network services, software versions, data types, and process dependencies, the platform builds a precise cyber-risk context for each asset
Risk scoring aligned with ISO 27005
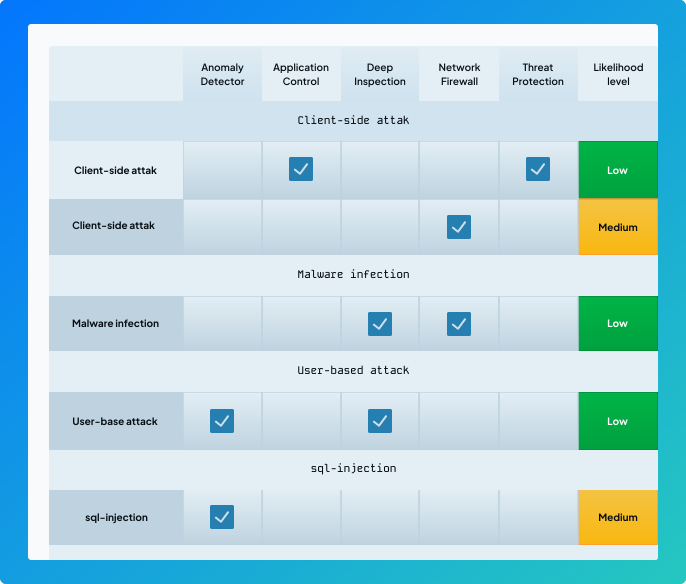
SecureVisio calculates cyber-risk using a clear, standards-based model: the final risk level is determined by multiplying the likelihood of a threat by the business impact of the affected asset. Likelihood reflects how easily existing controls can be bypassed, while impact considers the asset’s criticality and the sensitivity of the data it processes.
Fully configurable, organization-aware risk modeling.
Through customizable likelihood rules, asset criticality, dictionaries of threats and safeguards, and flexible matrix settings, SecureVisio adapts the risk calculation method to the specifics of your environment — ensuring that risk scoring reflects real operational impact.
Let Risk Analysis Drive
Security Decisions

RIsk analysis supports better incident and vulnerabilities handling

Automate risk management with safeguard recommendations

SecureVisio serves as a risk analysis foundation for NIS2 compliance

Incident, risk and avulnerability inside one platform lowers TCO


